
Browse by Category
Fiction
- Action & Adventure
- African American
- Anthologies
- Children's Fiction
- Classics
- Comics & Graphic Novels
- Coming of Age
- Contemporary
- Cultural & Regional
- Drama
- Erotica
- Fantasy
- General
- Historical Fiction
- Horror
- Humor & Satire
- Literary Fiction
- Mystery, Thriller & Suspense
- Poetry
- Religious & Inspirational
- Romance
- Science Fiction
- Short Stories
- War & Military
- Westerns
- Women's Fiction
- Young Adult
Non-Fiction
- Antiques & Collectibles
- Arts & Photography
- Biographies & Memoirs
- Business & Money
- Children's Non-Fiction
-
Computers & Technology
- Artificial Intelligence
- Computer Science
- Cybersecurity & Cryptography
- Data Science & Analytics
- Databases & Big Data
- Game Development & Design
- General
- Hardware & DIY
- Mobile App Development
- Networking & Cloud Computing
- Operating Systems
- Programming
- Robotics
- Software
- Software Engineering
- User Experience (UX) & Design
- Web Development & Design
- Cooking, Food & Wine
- Crafts, Hobbies & Home
- Education & Teaching
- Engineering
- General
- Health, Fitness & Dieting
-
History
- African History
- African History - North Africa
- African History - Sub-Saharan Africa
- American History
- American History - 20th Century
- American History - Civil War
- American History - Colonial Period
- Ancient History
- Asian History
- Asian History - China
- Asian History - India
- Asian History - Japan
- Asian History - Southeast Asia
- European History
- European History - Ancient Greece
- European History - Ancient Rome
- European History - Medieval
- European History - Modern
- European History - Renaissance
- General
- Middle Eastern History
- Military History
- Military History - Aviation
- Military History - Naval
- Social & Cultural History
- World History
- Humor & Entertainment
- Industrial Technology
- Language Learning
- Law
- LGBTQ+ Non-Fiction
- Literary Criticism
- Medical Books
- Parenting & Relationships
- Philosophy
- Politics & Social Sciences
- Reference
- Religion & Spirituality
-
Science & Math
- Agricultural Sciences
- Astronomy & Space Science
- Behavioral Sciences
- Biological Sciences
- Botany & Plant Science
- Chemistry
- Earth Sciences
- Engineering - Chemical
- Engineering - Civil
- Engineering - Electrical
- Engineering - Mechanical
- Environment
- General
- Geology
- Mathematics
- Nature & Ecology
- Oceanography
- Paleontology
- Physics
- Statistics
- Self-Help
- Sports & Outdoors
- Study Aids
- Sustainability & Green Living
- Textbooks
- Transportation
- Travel
- True Crime
- Urban Planning & Development
- Veterinary Medicine
- Writing & Publishing
Jump to Section
MixCache.com Total Access
Unlimited reading and audiobooks for every book published by MixCache.com.
Included titles carry the MTA badge.
Learn more →
The First Pen Testers
How Hackers Became an Industry, 1990-2005
About this book:
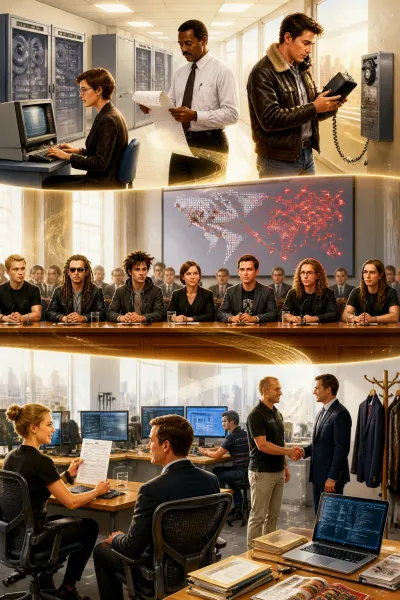 Before ransomware gangs and nation-state APTs dominated headlines, there were the tiger teams: Cold War engineers who broke into ARPANET mainframes to prove the Pentagon's digital crown jewels were made of glass. *The First Pen Testers* traces the improbable fifteen-year journey from those classified military exercises to the birth of a multi-billion-dollar industry—when phone phreaks and BBS sysops traded leather jackets for NDAs, taught Wall Street to speak buffer overflow, and turned "controlled trespass" into a compliance line item.
You'll sit in the Dirksen Senate Office Building as L0pht Heavy Industries tells Congress it can kill the Internet in thirty minutes—and watch senators reach for checkbooks instead of handcuffs. You'll witness the mailing-list wars that forged modern disclosure ethics, the toolmakers who automated the siege (SATAN, Nmap, Nessus, Metasploit), and the boutique consultancies—WheelGroup, @stake, Secure Networks—where hacker culture collided with venture capital, Sarbanes-Oxley, and the Big Four. Every chapter reveals a pivotal moment: the first zero-day markets, the birth of red teaming, the compliance mandates that turned rebellion into checkbox theater.
Deeply reported and driven by the voices of the practitioners who lived it, this is the definitive origin story of offensive security. Whether you're a CISO managing a red team program, a penetration tester curious about your lineage, or a leader wondering how the "kids in black T-shirts" became the immune system of the global economy, *The First Pen Testers* explains how we got here—and why the compromises forged between 1990 and 2005 still dictate every breach, every audit, and every boardroom conversation about risk today.
Table of Contents:
- Introduction
- Chapter 1 The Tiger Teams: Cold War Roots of Controlled Trespass
- Chapter 2 Phreaks, Modems, and the Underground BBS
- Chapter 3 The Legality Gap: The Computer Fraud and Abuse Act
- Chapter 4 From Anarchy to Audit: Early Network Assessments
- Chapter 5 SATAN Unleashed: The Automation of Vulnerability Discovery
- Chapter 6 The Rise of L0pht Heavy Industries: Hardware and Culture
- Chapter 7 Selling the Hack: The Birth of the Boutique Consultancy
- Chapter 8 The Commercial Frontier: WheelGroup and NetScan
- Chapter 9 Full Disclosure vs. Responsible Disclosure: The Mailing List Wars
- Chapter 10 L0pht Goes to Washington: Testifying Before the US Senate
- Chapter 11 Network Associates, Axent, and the First M&A Wave
- Chapter 12 @stake: Wall Street Money Enters Hacker Street
- Chapter 13 Scripting the Siege: The Emergence of Nessus and Nmap
- Chapter 14 Social Engineering: Weaponizing the Human Factor
- Chapter 15 Dot-Com Boom: Securing the Digital Gold Rush
- Chapter 16 The Exploit Economy: Zero-Days as Commodities
- Chapter 17 Methodology Matters: The Quest to Standardize Infiltration
- Chapter 18 From Hobbyist to Suit: Corporate Culture Shock
- Chapter 19 Post-9/11 and Critical Infrastructure: Homeland Defense Reframes Hacking
- Chapter 20 Metasploit and the Democratization of Exploitation
- Chapter 21 The Compliance Mandate: Sarbanes-Oxley, HIPAA, and Checkbox Security
- Chapter 22 Red Teams vs. Blue Teams: War Games in the Boardroom
- Chapter 23 The Big Four Move In: Professional Services Absorb the Rebel
- Chapter 24 Ethics, Certifications, and the CISSP Era
- Chapter 25 The Industrial Complex: The Legacy of the First Pen Testers
Author:
Published By:
Type:
Nonfiction
Sample:
Order:
Click to buy this ebook:
Buy Now